Lightwell Software Supply Chain Security Workshop
You walk one trusted software supply chain on a dedicated OpenShift cluster. For one promoted Java application, you retain evidence of base-image verification, dependency selection, source changes, build controls, application signatures, runtime signature enforcement, and an inventory and policy assessment.
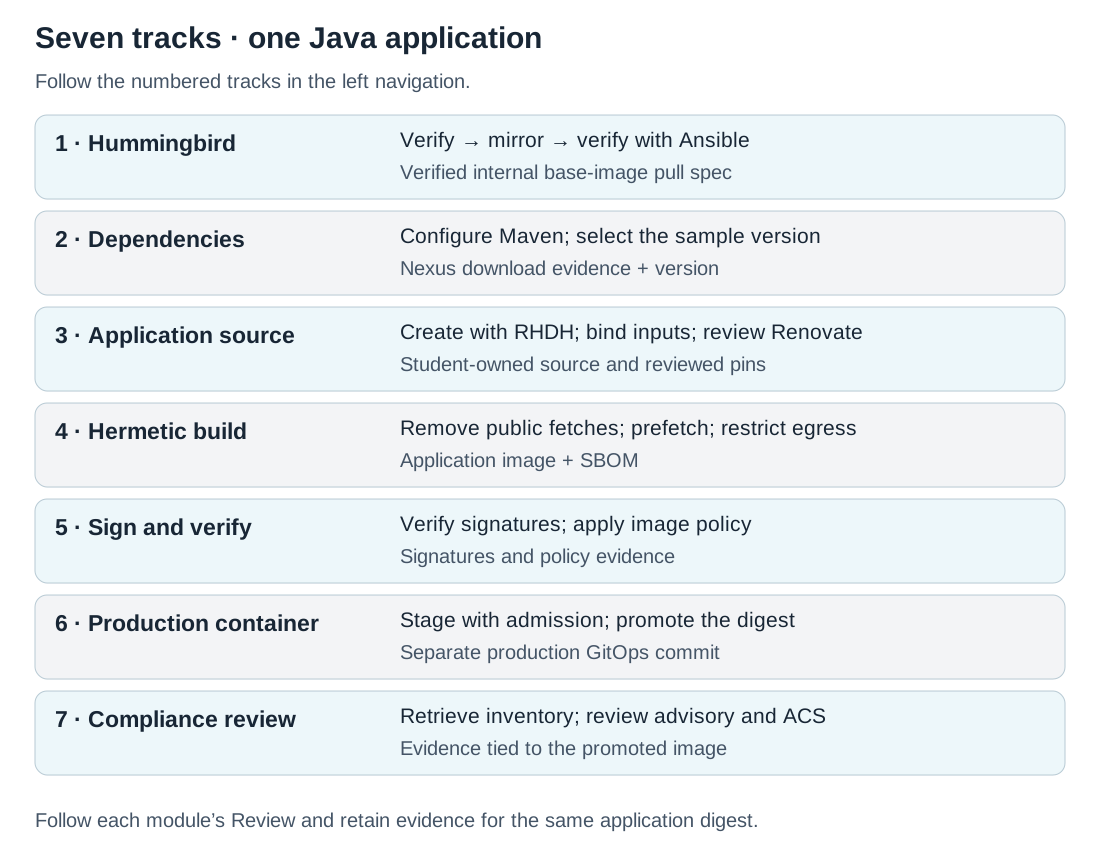
The workshop has seven tracks. You verify a Hummingbird base, consume seeded Lightwell dependency coordinates, own the application source, build hermetically, sign and verify the application, promote its digest, and review compliance evidence at a point in time.
The sample advisory LW-DEMO-0002 and .rhlw-* JAR are simulation fixtures with unchanged upstream class files; you do not apply a real security patch. Track 5 produces image signatures and signature-policy reports, not build-provenance attestations. Track 7 stores application and library CycloneDX SBOMs and sample OSV in Trusted Profile Analyzer (TPA), inspects OpenVEX locally, and records an ACS assessment of the promoted image. Ongoing organization-wide monitoring requires additional operational work.
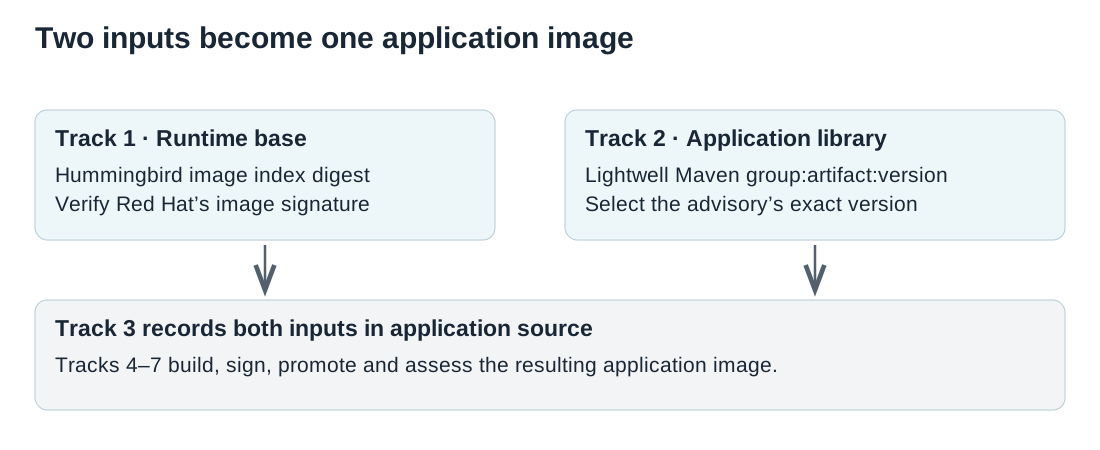
You build an example application that serves a greeting over HTTP: a request to /api/greeting returns a hello message for the name you send. The application is written in Java and built with Maven, and that Maven build is the one you complete. Maven compiles the application and downloads its libraries. settings.xml points Maven at the enterprise proxy on this cluster, an in-cluster Nexus. You then use the library at an exact .rhlw-* version, which models a Lightwell security-backport coordinate. Later modules sign and admit the assembled application image and compare that library coordinate with the sample advisory.
We use Java, Maven, an artifact manager such as Artifactory, and in-cluster Gitea. On this cluster the artifact manager is Nexus. Customers often run Artifactory for that same proxy. We call out Python and JavaScript. You read the callout and continue with Java, Maven, Nexus, and Gitea.
-
Python uses
pip.confthe way this workshop usessettings.xml. The remediated version suffix looks like1.0.0+rhlw.00001on arequirements.txtline. -
JavaScript libraries follow the same pattern: an enterprise npm registry, and an exact package version. You can describe that pattern to a customer. This cluster has no npm exercise.
Hands-on work starts at 1 Build a verified base-image mirror with Ansible. There you complete an Ansible workflow in Showroom that verifies, mirrors, and verifies the Hummingbird index on the bastion.
What a trusted software supply chain proves
A trusted software supply chain (TSSC) is the set of controls that let you answer three questions for every production container. What went into the image? Who built it and signed it? Are known vulnerabilities remediated, without treating the public internet as a trusted input?
On OpenShift, Red Hat TSSC is those controls as products you will actually open in this workshop:
-
Application image signing and verification, in Red Hat Trusted Artifact Signer
-
A system of record for SBOMs and advisories, in Red Hat Trusted Profile Analyzer
-
Runtime and pipeline policy, in Red Hat Advanced Cluster Security and in Conforma, the Enterprise Contract CLI
ec -
Promotion by Git, in OpenShift GitOps
-
A golden path for the application repo, in Red Hat Developer Hub
The same stack is what Red Hat Trusted Application Pipeline describes. You will not install that pipeline as a product. You will use the pieces above, on this cluster, under the names the modules use.
TSSC does not start when a pipeline runs. It starts with inputs you can name: a signed runtime base, application libraries from a trusted repository, and source that records both exact versions. An exact version is the full name written in source. For the base, that name is the Hummingbird pull spec, digest included. For a library, that name is a version such as 3.14.0.rhlw-00001. Hummingbird is the base. Lightwell is the library layer.
Lightwell Network and Lightwell Clearinghouse
Lightwell is the Red Hat and IBM initiative that maintains third-party application dependencies: libraries, frameworks, build tools, and the transitive dependencies those pull in. A scanner can name a CVE that your team cannot upgrade away from, because of certification, compatibility, or a release window. Lightwell supplies a security-only fix on the version you already run.
Product reference checked on 2026-11-10: Lightwell offers Network and Clearinghouse subscriptions. Clearinghouse is generally available to eligible organizations for approved scope; this is not a promise of coverage for every package or vulnerability. Confirm eligibility, entitlements, and current service terms with Red Hat’s current offering information.
| Offering | Customer use | Workshop coverage |
|---|---|---|
Lightwell Network |
Self-service access to eligible signed dependencies and remediations. It has three repository tiers: Validated, Remediated, and Predisclosure. |
Tracks 2, 3, and 7 use seeded Validated and Remediated coordinates through Nexus. You select a sample OSV fixed version and retain SBOM and advisory evidence. See repository tiers and Java configuration. |
Lightwell Clearinghouse |
Includes Network and adds customer-specific requests within approved scope, vulnerability verification and disclosure coordination, applicable anonymized request visibility, and Security TAM services. |
A customer-specific artifact still needs repository, source, build, and evidence controls. The lab does not exercise a Clearinghouse engagement or an embargo. |
Predisclosure is a Network repository tier, not an exclusive Clearinghouse capability. Its versions add -nXXXX after the remediation suffix, for example 5.3.17.rhlw-00001-n0001. Follow the applicable access and redistribution terms; this is a reference topic, with no third repository exercise. See repository version suffixes.
Keep the layers separate when you talk to a customer. Lightwell covers application-layer dependencies. RHEL, OpenShift, and ACS cover the operating system and the platform. Hummingbird, part of Red Hat Hardened Images, is the runtime foundation the container starts from. For the evidence and repository concepts, see Lightwell concepts.
How this workshop maps to TSSC
Each gated module exists so you can see the control, not only so you can fill in a ConfigMap. Use the table as a glossary while you work: the objective, the module where you will meet it, and what changes if the customer is on Network or on Clearinghouse.
| TSSC objective | Where you observe it | Lightwell Network / Clearinghouse |
|---|---|---|
Trusted runtime input (signed minimal base) |
Track 1 Ansible workflow: verify the published index, mirror from the bastion, verify the internal digest |
Complementary. Hummingbird is not a Lightwell GAV. Clearinghouse does not replace Hardened Images. |
Trusted library input (enterprise proxy, not the public index) |
2.1 Maven |
Network: this is how customers consume |
Exact-version remediation (not "upgrade to latest") |
2.2 OSV |
This exercise uses sample OSV. In customer delivery, a Predisclosure version may be available before a public advisory; retain its full suffix and respect distribution restrictions. |
Source of truth binds those exact versions |
3.1 student-owned Gitea; 3.2 dest |
Renovate, with MintMaker described in the Konflux reference, opens the pull request that brings a new Network or Clearinghouse version. You merge that pull request. |
Hermetic production of the image (source, prefetch, network) |
Lightwell GAVs resolve from the internal proxy after egress is denied. Clearinghouse does not add a public fallback. |
|
Integrity of the app artifact (signatures and policy) |
You sign the application image. Supplier provenance verification for real dependencies is a separate customer control; the seeded JAR has no Red Hat-signed provenance claim. |
|
GitOps selects the digest; runtime policy checks its trusted-key signature |
The native PublicKey path checks the admission key and signed repository identity. It is not a one-digest allowlist and does not enforce the recorded Fulcio subject. |
|
Point-in-time compliance evidence for one promoted image |
Store application/library CycloneDX and sample OSV in TPA; inspect OpenVEX locally. Assess the same image with ACS. Customer advisory access, refresh, and incident response need separate operational design. |
What this workshop does not include
You walk one supply chain on this OpenShift environment. We use Java, Maven, an artifact manager such as Artifactory, and in-cluster Gitea. On this cluster the artifact manager is Nexus, and the application is a Java greeting service. The table is here so you do not lose time looking in the console for a product this cluster deliberately left out. When a customer asks about that product, the right-hand column is the sentence you use, and the module where this workshop already practiced the underlying control.
| Not in this workshop | What you do instead |
|---|---|
Hosted Konflux |
Builds run as OpenShift Pipelines (the Task and BuildConfig names on the cluster). Names you may hear in a customer conversation are in Konflux mapping. Do not install Konflux. |
A physical air-gap or data diode |
This environment stays on the network. 5.3 is the key-based sign and verify procedure. Disconnected transfer planning collects public evidence only. It does not mirror TUF, transfer images/signatures, or verify a destination; design and test that procedure separately. |
Building Project Hummingbird images |
You verify and consume published Red Hat Hardened Images. You do not rebuild the Fedora factory that produces them. |
FIPS certification in the lab |
FIPS is a product claim on the image you consume. This workshop does not rebuild an image to produce FIPS evidence. |
JFrog Artifactory, or a Python (FastAPI) application |
We use Java, Maven, Nexus, and in-cluster Gitea. Artifactory is the artifact manager customers often run; you do not install it on this cluster. We call out Python. You do not scaffold a second app. |
A live Clearinghouse membership, member-specific GAV, or embargo window |
You practice a simulated post-disclosure Network version and the TSSC controls Clearinghouse would reuse (private proxy, exact version, system of record). You do not request a member-only package or sit inside a real embargo on this cluster. Concept: Lightwell concepts. |
A customer proof-of-value or certification exam |
This is a guided workshop. You practice the flow here. Internal enablement is scored after the event. It is not a live PoV on this environment. |
A production virtual machine |
You promote a signed container digest through GitOps (6.1, 6.2). A suitable VM container runtime can run the same application digest. A bootc host needs a separately built and verified bootable OS image with its own digest. Satellite manages and distributes content; it is not the application runtime. No VM implementation is included here. |
Module Validation
Each Track 5 module has an in-cluster Validate Job in the namespace lw-poc-validate. The Job grades the live object you changed and a report ConfigMap token that shows this module was completed. Do the Exercise. Fill the token. Run the Job. If the Job already exists, delete it, create it again from ConfigMap validate-job-templates, and read the logs. There is no Solve, feel free to retry until you succeed.
Track 1 uses the Review in its guide: compare the mirrored image with the recorded starting state and inspect the playbook’s signature-verification evidence. The successful Ansible workflow publishes its report; you do not fill its token manually or run a separate validation Job. Track 2 uses Maven command output for its review. Track 3 uses repository inspection, comparisons with the earlier image and dependency evidence, and review of the merged Renovate pull request. Track 4 uses the existing Review sections to inspect Git source, live Pipeline and NetworkPolicy output, and saved build and SBOM evidence. Tracks 3 and 4 have no validation Job or report token to submit. Track 6 uses terminal checks of published Git configuration, Argo CD state, runtime policies, and signed-versus-unsigned evidence, with no validation Job or report token to submit. Track 7 compares the promoted digest with a retrieved TPA inventory, interprets the sample library advisory, and inspects ACS policy output for the same image. It uses terminal evidence and a local written report, with no validation Job or report token. Track 5 provides its own report keys and Job commands.
Before you start
You read this guide in the RHDP Showroom, which is the lab nav plus an embedded terminal. ansible-playbook, oc, cosign, oc-mirror, and ec are already on PATH. Leave GitHub out of the lab: do not curl it for CLIs, and do not use it as the lab git remote. Gitea is in-cluster.
Discover URLs, digests, and passwords from the lab-* ConfigMaps. On a module that has a Validate Job, that Job in lw-poc-validate is the Check. Never commit credentials: LW_USERNAME, LW_PASSWORD, student_password, or cosign.key.
Official documentation
Open the product docs when a customer asks where a claim is written. They do not replace a Check. The Check is what this cluster grades.
-
Lightwell (Network and Clearinghouse models)
-
Lightwell Network: patch delivery lifecycle (ends at public Disclosure / OSV / VEX)
-
Lightwell Network: choose Validated, Remediated, or Predisclosure
-
Technologies behind Trusted Application Pipeline (RHTAS, RHTPA, RHDH)
-
Trusted Artifact Signer deployment guide (includes Conforma /
ec)
Start here
Open 1 Build a verified base-image mirror with Ansible when you are ready to make the first change.
If you are delivering the workshop rather than taking it, the maps sit beside this module. Consultants: delivery map, Konflux mapping, disconnected transfer. Instructors: two-day grouping, which is an envelope for the room. After the event: internal enablement checklist. Concepts you may want open in another tab: Lightwell concepts, acronym glossary.
Keep your work between sessions
Showroom mounts persistent storage at /home/lab-user. Keep the application and stage/production GitOps clones in /home/lab-user/lightwell-workspace; the exercises use absolute paths so temporary registry login settings cannot redirect your work. Keep the existing evidence directories (lightwell-build-evidence, lightwell-signing-evidence, and any Track 7 evidence) and lab-trust under that same home. /tmp is only for files you can recreate from Git or cluster state. The home volume survives a Showroom pod replacement, but it is not a backup after your claim or its PVC is deleted.
When you return, open a new terminal, confirm oc whoami, and rerun the current module’s discovery commands to restore shell variables. Showroom initializes Git authentication on startup; if a push cannot authenticate, use the Git setup instructions in module 3.2. Repeat the registry login before signing or copying images, because its temporary credentials may be gone. Inspect git status in each existing clone before continuing. Do not reclone over it, reset it, or regenerate a signing key that is already present. Compare saved image digests with the live image before reusing verification evidence.
If you started with an older guide and the old /tmp clone still exists, move that directory into /home/lab-user/lightwell-workspace only when the destination does not exist; moving the whole clone preserves uncommitted files and .git. Also move any track6-*-verification.json and unsigned-test event evidence into /home/lab-user/lightwell-signing-evidence before a restart. If both old and new directories exist, inspect them and reconcile your edits before proceeding. After /tmp has been lost, clone from the student-owned remote to recover pushed commits and repeat the evidence-producing steps. Uncommitted files lost with /tmp cannot be recovered from Git.