1.2 Mirror into the trust boundary
On this page you prove that the Hummingbird image you verified in the public catalog now sits on this cluster’s registry, and that cosign still accepts its signature there.
Track 1 is the base. This is the second page. 1.1 Verify Hummingbird checked the published pin. The Nexus Docker repository hummingbird-mirror starts empty. You finish the ImageSet, start Job oc-mirror-learner, and verify the dest pull spec.
Why this control exists
Later builds, GitOps, and admission pull the runtime base from inside the enterprise. The coordinate they use is this internal dest, and you can still verify it. You run the mirror so the signature arrives with the image.
In a customer engagement, a bastion host runs oc-mirror into the customer’s registry. On this cluster the dest is in-cluster Nexus, hosted Docker repository hummingbird-mirror, exposed by Route registry-lightwell-repo. The Route host is specific to your cluster. You read it from userinfo. You still write the ImageSet, and you still start the run.
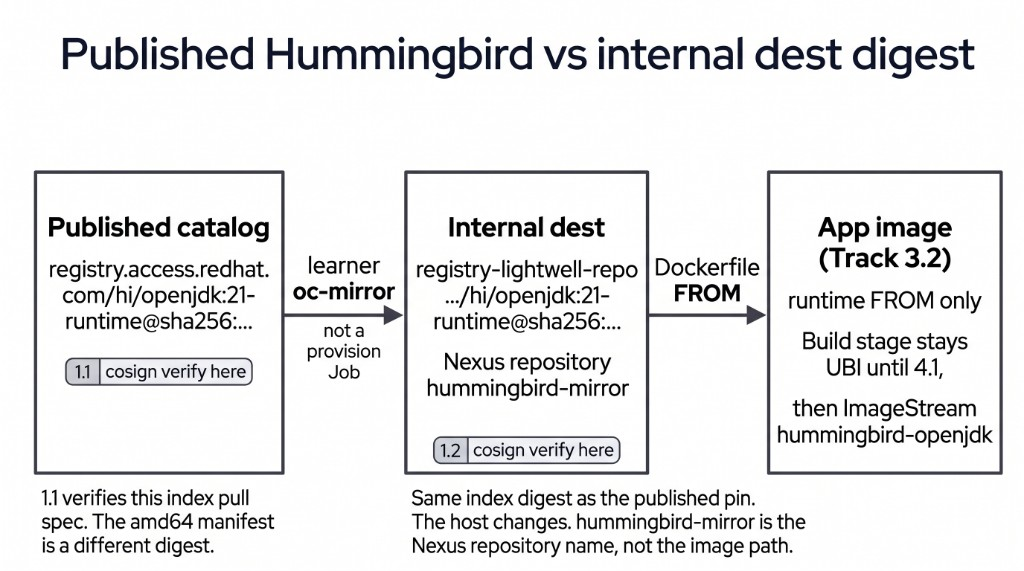
The figure has three coordinates. This page is the middle box. The badge there marks the cosign verify you run after the Job. The arrow into that box is Job oc-mirror-learner, which you start. The left box is the published catalog from 1.1. You copy that pull spec into the ImageSet. The index digest stays the one you verified. The host becomes the Route host. The image path stays hi/openjdk. The label hummingbird-mirror names the Nexus repository that stores the image. The right box is Track 3, where the application Dockerfile FROM uses the dest pull spec.
Lightwell Network and Lightwell Clearinghouse Premier remediate application libraries. Those libraries arrive through the Maven proxy in Track 2, as a separate input from this ImageSet. A Premier library still runs on this dest Hummingbird. Track 3 binds FROM to the dest pull spec you record here.
|
A Hummingbird Python runtime follows the same pin-and-mirror. This Check scores the Java |
|
A customer dest is often an Artifactory Docker remote or a local cache. The work is the same: an ImageSet, |
Learning objectives
By the end of this module, you will be able to:
-
Put the Hummingbird pull spec from userinfo into
ImageSetConfiguration -
Start Job
oc-mirror-learnerand read the dest pull spec from its signature-copy log -
Verify that dest pull spec with the same Red Hat Hardened Images key as 1.1
The empty dest
ConfigMap demo-userinfo-lightwell-repo in namespace lightwell-repo holds the dest coordinates. Four fields matter. dest is the Route host. repo is the Nexus Docker repository name, hummingbird-mirror. docker is docker:// plus that host, which is the destination the Job already uses. pre_mirror is false while the scored image is still absent.
Success is those four lines, with pre_mirror=false.
oc -n lightwell-repo get configmap demo-userinfo-lightwell-repo \
  -o jsonpath='dest={.data.dest_registry_host}{"\n"}repo={.data.dest_registry_repo}{"\n"}docker={.data.dest_registry_docker}{"\n"}pre_mirror={.data.oc_mirror_pre_stage_scored_image}{"\n"}'
The file you finish is an ImageSetConfiguration, API mirror.openshift.io/v2alpha1. It tells oc-mirror which images to copy. On this cluster it lives in ConfigMap imageset-configuration, same namespace, key imageset-config.yaml. The seed names one additional image, and that name is still the placeholder REPLACE_ME_HUMMINGBIRD_PULLSPEC.
Success is a short YAML document that still contains REPLACE_ME_HUMMINGBIRD_PULLSPEC.
oc -n lightwell-repo get configmap imageset-configuration \
  -o jsonpath='{.data.imageset-config\.yaml}'
ConfigMap oc-mirror-tooling in the same namespace holds a worked example on key example-imageset.yaml. That example names ubi9/ubi-minimal. The scored file is imageset-config.yaml on ConfigMap imageset-configuration. The Check requires the Hummingbird pull spec from userinfo. An ImageSet that still names ubi-minimal fails the Check, including a paste of this example over the scored key.
oc -n lightwell-repo get configmap oc-mirror-tooling \
  -o jsonpath='{.data.example-imageset\.yaml}'
# Worked example ONLY — ubi-minimal. The scored ImageSet must be the Hummingbird digest pin.
kind: ImageSetConfiguration
apiVersion: mirror.openshift.io/v2alpha1
mirror:
additionalImages:
- name: registry.access.redhat.com/ubi9/ubi-minimal:latestYour change
Read the pull spec you verified on 1.1. Success is one line: registry.access.redhat.com, hi/openjdk, and @sha256:. That digest is the image index. The amd64 manifest you recorded beside it is a different sha256. The ImageSet uses this pull spec.
oc -n lightwell-repo get configmap demo-userinfo-lightwell-repo \
  -o jsonpath='{.data.hummingbird_source_pullspec}{"\n"}'
Edit ConfigMap imageset-configuration in namespace lightwell-repo. Set mirror.additionalImages[0].name to that pull spec. The command is oc -n lightwell-repo edit configmap imageset-configuration. Change that name line. Leave the rest of the key in place.
The seed looks like this:
kind: ImageSetConfiguration
apiVersion: mirror.openshift.io/v2alpha1
mirror:
  additionalImages:
    - name: REPLACE_ME_HUMMINGBIRD_PULLSPEC
The ImageSet stays a single additionalImages entry. The Job, in the next section, mirrors that name and then copies the signatures. You change the pull spec here.
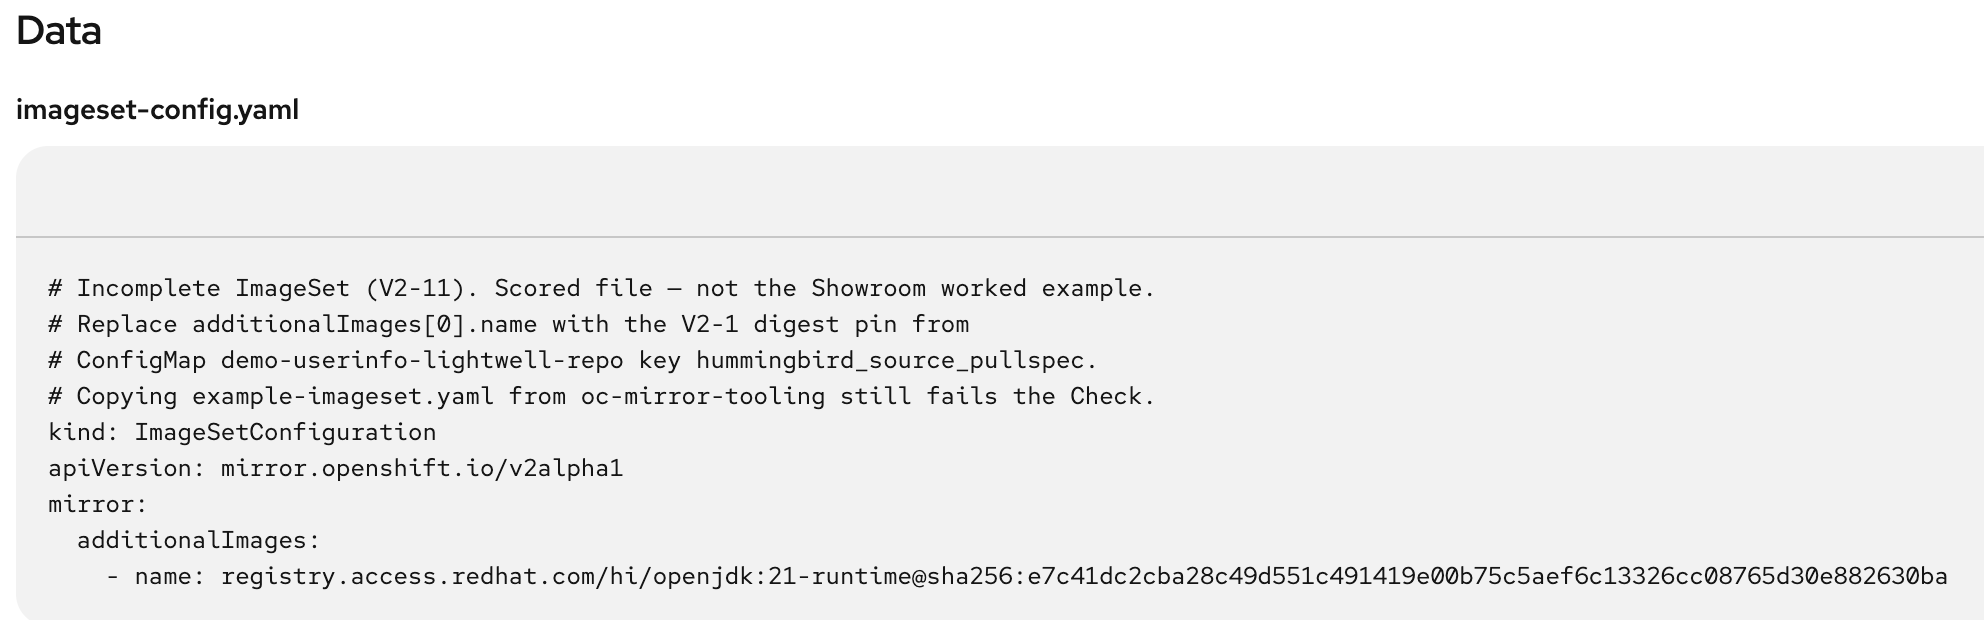
The capture is ConfigMap imageset-configuration after that edit. Read name as one pull spec, from registry.access.redhat.com through the end of the digest. A narrow window wraps the value onto the next line. The digest is still part of name.
Confirm the placeholder is gone. Success is the line placeholders gone.
oc -n lightwell-repo get configmap imageset-configuration \
  -o jsonpath='{.data.imageset-config\.yaml}' | grep -E 'REPLACE_ME' \
  && echo 'STILL HAS PLACEHOLDERS' || echo 'placeholders gone'
Run oc-mirror
oc-mirror is already on the Showroom PATH. The scored run is Job oc-mirror-learner. The Job manifest is key job.yaml on ConfigMap oc-mirror-tooling. That manifest already mounts the dest credentials and the workspace volume. You create the Job from that key, as stored. Provision leaves the Job uncreated until you do.
The Job has two containers. The init container oc-mirror copies the image onto dest. The stored command mirrors that image and leaves --remove-signatures out of the arguments. The signature tags are the next container: copy-signatures runs cosign copy from the published pin to the dest pull spec and writes .sig, .att, and .sbom tags beside the image. Nexus stores those objects as tags.
If a previous attempt still owns the name, delete it first. Success is job.batch/oc-mirror-learner created.
oc -n lightwell-repo delete job oc-mirror-learner --ignore-not-found
oc -n lightwell-repo get configmap oc-mirror-tooling \
  -o jsonpath='{.data.job\.yaml}' | oc create -f -
The mirror and the signature copy can take several minutes. Success is condition met for complete. The wait allows 20 minutes.
oc -n lightwell-repo wait --for=condition=complete job/oc-mirror-learner --timeout=20mRead both containers. The init container oc-mirror is the image copy. The container copy-signatures is the tag copy.
The oc-mirror log prints two lines that are expected for this ImageSet. The name you set is one pull spec: the tag 21-runtime and the index digest from 1.1. The warning includes has both tag and digest : using digest to pull, but tag only for mirroring. The next line says No images by digests were mirrored. Skipping IDMS generation. IDMS is an ImageDigestMirrorSet, the object that would redirect a later digest pull to a mirror. This ImageSet is mirrored under the tag, so oc-mirror skips that object. The copy still used the index digest from 1.1.
In the copy-signatures log, success is a line that starts with DEST_PULLSPEC=. The value is the dest host, the path hi/openjdk, the tag, and the same index digest as the published pin. Copy that whole line. The repository name hummingbird-mirror does not appear in it. The Check is cosign verify on that dest pull spec.
oc -n lightwell-repo logs job/oc-mirror-learner -c oc-mirror
oc -n lightwell-repo logs job/oc-mirror-learner -c copy-signatures
Check
Verify the dest pull spec with the same Red Hat Hardened Images public key as 1.1. Paste the DEST_PULLSPEC= value into the variable below. Dest TLS is the lab registry, so the command allows an insecure registry. --insecure-ignore-tlog skips the transparency log, and this cosign warns that it skipped the log.
Success is the same two checks, printed for the dest host: the cosign claims were validated, and the signatures were verified against the specified public key.
# Fill DEST_PULLSPEC from the copy-signatures log (DEST_PULLSPEC=...).
export DEST_PULLSPEC='REPLACE_ME_DEST_PULLSPEC'
cosign verify \
  --allow-insecure-registry \
  --key https://security.access.redhat.com/data/63405576.txt \
  --insecure-ignore-tlog \
  "${DEST_PULLSPEC}"
That output is how you see the signature on dest. The Validate Job grades ConfigMap imageset-configuration in lightwell-repo (the userinfo pull spec, with the placeholder gone), a completed Job oc-mirror-learner, .sig tags on the dest image, and the report key below. Verifying registry.access.redhat.com again is the 1.1 Check. Track 3 sets the application FROM to the dest pull spec you just verified.
The Job also grades ConfigMap report-02-hummingbird-mirror key learner_runs_mirror. Set it to learner-mirror. Empty or REPLACE_ME fails even if cluster state is correct. Do not copy validate-docs.
oc -n lw-poc-validate edit configmap report-02-hummingbird-mirrorThe scored Check is Job validate-02-hummingbird-mirror in lw-poc-validate. Direct nav URLs still work (honor system). Unlimited retries. There is no Solve.
oc -n lw-poc-validate delete job validate-02-hummingbird-mirror --ignore-not-found
TPL='job-02.yaml'
oc -n lw-poc-validate get configmap validate-job-templates \
  -o go-template="{{ index .data \"${TPL}\" }}" | oc create -f -
oc -n lw-poc-validate logs -f job/validate-02-hummingbird-mirror
Expect CHECK PASSED: before you continue. CHECK FAILED: names the object to fix. Delete the Job and create it again as often as you need.
Official documentation
-
Mirroring images with the oc-mirror plugin v2 (
ImageSetConfigurationmirror.openshift.io/v2alpha1,additionalImages) -
Verify the integrity of Red Hat Hardened Images (same public key as 1.1, now against the dest pull spec)
Key takeaways
-
The signed base lives on the internal dest because you ran the mirror.
-
The dest pull spec keeps the index digest from 1.1 and uses the Route host. The image path is
hi/openjdk. -
The Job copies the image, then copies
.sig,.att, and.sbomtags, because this Nexus dest stores signatures as tags. -
Lightwell libraries use the Maven proxy. Track 3 binds
FROMto this dest pull spec.